
Website security protection
Website security protection
Website security protection is achieved through frequency limits, IP whitelist and blacklist, UA checks, and memory threshold to intercept abnormal access.
Entry Path
Top menu of the background → 'Function' → 'System Function' → 'Website Security Protection'. Actual address:/system/plugin/system/limiterrequires administrative privileges(canAdmin)
Function description
The page includes the master switch for protection, spider release, empty UA/empty Refer restriction, temporary ban strategy, IP whitelist and blacklist, specific UA restriction, path prefix exclusion and memory limit, and provides a list of temporarily banned IPs.
Screenshot of the interface
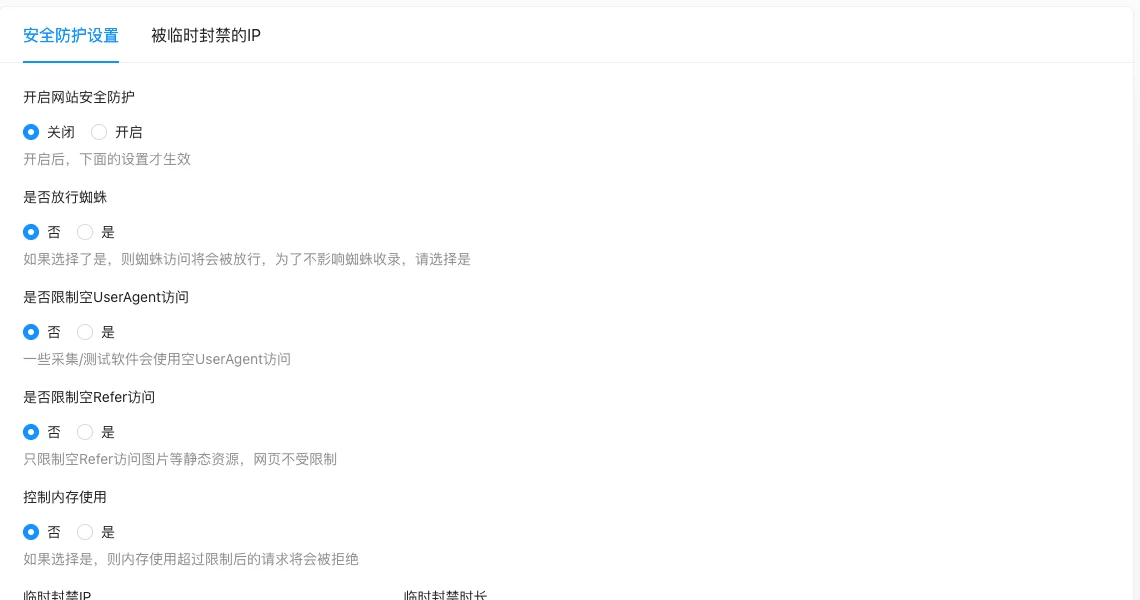
Setting item description
| Setting items | function | Value / Default | How to select / Fill in suggestions | Impact / Note |
|---|---|---|---|---|
| Enable website security protection | Master switch | radio: Off (default) / On [实测] | Enable when attacked by data collection or CC attack | All settings below will not take effect after closing |
| Whether to allow spider release | Whether to not intercept search engine spiders | radio: No (实测) / Yes [实测] | Recommend selecting 'Yes' | Selecting 'No' may affect inclusion |
| Limit empty UserAgent | Block requests without UA | radio: No / Yes,实测 'No' [实测] | Can block some collection tools | — |
| Limit empty Refer | Block static resource requests with empty source | radio: No / Yes,实测 'No' [实测] | Used when anti-hotlinking | Only affects resources, does not affect the web page |
| Temporarily disable IP | Access frequency threshold | Number, default 100 times per 5 minutes [i18n]; actual 0 [actual] | Set according to the peak usage of normal users | 0 or leave blank to use the default 100 |
| Temporary disable duration | Duration after triggering the disable | Number, default 1 hour [i18n]; actual 0 [actual] | Generally 1-24 hours | — |
| Whitelist IP | Allow specified IP/segment | Text field, one per line, supports CIDR [source code] | Add office/home IP | Mistake may block yourself outside |
| Blacklist IP | Deny specified IP/segment | Text field, one per line, supports CIDR [source code] | Add confirmed malicious source | — |
| Restrict specific UserAgent | Deny specified UA | Text field, one per line [source code] | Block known collection UA | — |
| Exclude specific path prefixes | These paths are unrestricted | Text field, one per line, such as/api[Source code] |
Allow API or verification files | Avoid affecting normal interfaces |
| Memory limit | Deny requests when memory exceeds the threshold | radio: No / Yes [source code] | Enable when server memory is tight | — |
| **Use memory percentage | Memory threshold | Number 50-100, default 90 [i18n] | Default 90 is enough | Setting it too low may reject normal requests |
Detailed explanation of configuration items
IP and path rules
Condition for occurrence: Effective after enabling protection [Source code].
IP whitelist/blacklist, UA list, and path prefixes are parsed line by line; IP supports single address and CIDR (such as192.168.2.0/24)[source code].
Recommended value: The whitelist should add your own management IP first; add path exclusion/apifor interfaces that need to be allowed through.
Consequences of filling in incorrectly: Incorrect CIDR writing may reject a large number of normal users, or block administrators from the background.
Memory limit (duplicate field)
Condition for occurrence: Duplicate option and percentage fields related to memory limit appeared in the source codename(mem_limit/mem_percent), Different i18n keys, but both control memory limit display [COMPUTED].
influence: Fill in the group displayed on the interface as a reference; both groups exist simultaneously, which is a frontend repeat rendering, check whether it takes effect after filling in the front end
Operation steps
- Enter Function → System Function → Website Security Protection
- Turn on the master switch.
- Set spider pass and empty UA/Refer strategy
- Configure blocking thresholds, IP list, and path exclusion
- Click 'Submit' to save and observe the effect on the 'IPs Temporarily Blocked' tag
Operation steps
- Enter Function → System Function → Website Security Protection
- Turn on the master switch.
- Set spider pass and empty UA/Refer strategy
- Configure blocking thresholds, IP list, and path exclusion
- Click 'Submit' to save and observe the effect in 'Temporarily Banned IPs.'
Applicable scenarios and suggestions
- Turn on when attacked by collection or CC attacks and配合 IP blacklist.
- It is recommended to keep 'Yes' for bypassing spiders, otherwise it may affect indexing.
Points to note
- A wrong whitelist may block yourself or normal users outside.
- Setting the memory limit too low may mistakenly reject normal requests.
- Excluding path prefixes can be used to bypass APIs or verify files, to avoid collateral damage.