
Administrator group
📅 November 21, 2026
👁️ 0
Administrator group
The group management is used to define the permission range of background accounts, corresponding tocanAdmin/canSuperand other permission controls.
Entry Path
Top menu of the background → 「Admin」→「Group management」. Actual address:/system/account/group/listrequires administrative privileges(canAdmin)
Function description
Page displays the group list (ID, group name, status), supports adding, modifying, and deleting groups. The system includes a Super Administrator group.
Screenshot of the interface
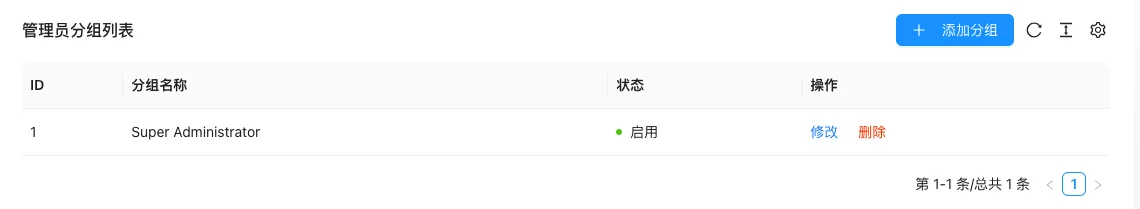
List field description
| field | Meaning | Value or source | Impact on the operation |
|---|---|---|---|
| ID | Group number | Back-end record, read-only | Used for identification and filtering, cannot be directly edited |
| Group name | Permission group name | Back-end record, read-only | Used for identification and filtering, cannot be directly edited |
| Status | Enable / Disable | Back-end record, read-only | Used for identification and filtering, cannot be directly edited |
| Operation | Modify / Delete | Back-end record, read-only | Used for identification and filtering, cannot be directly edited |
| Meaning | |||
| :— | :— | ||
| ID | Group number | ||
| Group name | Permission group name | ||
| Status | Enable / Disable | ||
| Operation | Modify / Delete |
Operation steps
- Enter 'Admin → Admin Groups'.
- Click 'Add Group' to create a new group.
- In the group configuration, check the backend menus allowed to be accessed.
- Go to 'Admin List' and assign the account to this group.
Applicable scenarios and suggestions
- Content editing should only grant related content menu permissions, do not grant system and multi-site permissions.
- The multi-site feature requires
canSuperPermissions, available only to super administrators.
Points to note
- Too broad permission configuration can lead to misoperations and security risks.
- Deleting a group still in use by an account will cause these accounts to lose permissions.